NCache Security
Active Directory / LDAP / gMSA, TLS, Data Encryption
NCache protects distributed caches with layered security (authentication, authorization, encrypted communication, and data encryption) without compromising performance or scalability. It integrates with Microsoft Active Directory and LDAP, so you manage access centrally, and supports password-less gMSA/Kerberos authentication for Windows applications. Security works on Windows Server on-premises and in Azure, AWS, and Google Cloud, as well as on Linux, Docker, and Kubernetes.
- Active Directory / LDAP Authentication: Applications and admins authenticate with existing directory identities, and NCache servers enforce their permissions.
- Windows gMSA Authentication: Password-less, Kerberos-based authentication for Windows client applications.
- Cloud Authentication: Use managed or existing Microsoft Active Directory in Azure, AWS, and Google Cloud, with no separate identity system.
- Role-Based Access Control (RBAC): Node-level and cache-level permissions separate server administration from application data access.
- TLS / mTLS: Encrypt traffic between applications, servers, cluster nodes, and Bridges, with NCache-managed or enterprise-issued certificates.
- Data Encryption: AES encryption in the client, so data stays encrypted in server memory and during replication.
- Secure Administration: Protected access to NCache Management Center and PowerShell.
- Cross-Platform Security: Windows, Linux, Docker, and Kubernetes.
Active Directory & LDAP Authentication
NCache authenticates Node Admins and Cache Users against Microsoft Active Directory or other LDAP-compatible directory services, on Windows or Linux cache servers. You grant NCache permissions to existing domain users and groups, so there is no separate NCache user directory to maintain, and your existing password policies and account restrictions still apply.
- Primary and secondary LDAP domain controllers.
- Secure LDAP connections where configured.
- Authentication and authorization enforced at the cache server.
- Optional caching of authenticated credentials to reduce repeated directory validation in a running process, depending on your security policy.
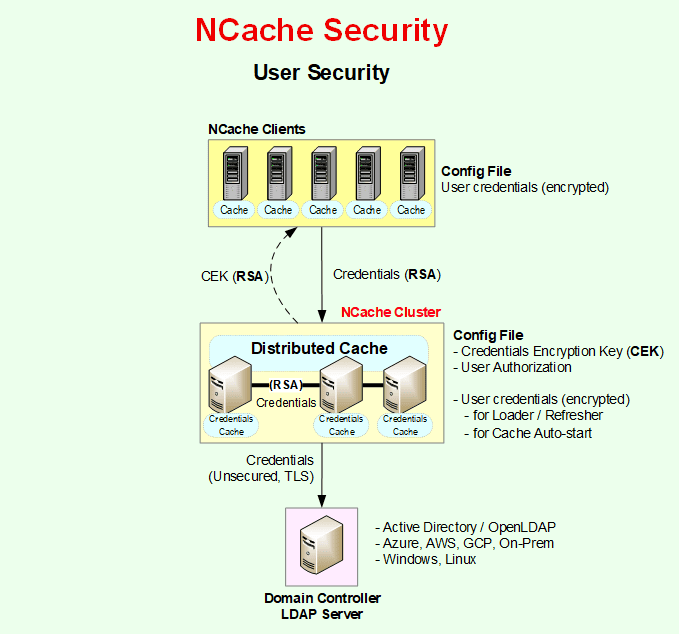
Connect using Active Directory/LDAP credentials:
using Alachisoft.NCache.Client;

var options = new CacheConnectionOptions();
options.Security = SecurityOptions.CreateWithCredentials("your-username", "your-password");

ICache cache = CacheManager.GetCache("demoCache", options);
In production, obtain credentials from a secure source rather than hardcoding passwords.
Windows gMSA Authentication
Client applications can authenticate with a Windows Group Managed Service Account (gMSA) instead of storing usernames and passwords in configuration files. Active Directory generates and rotates the gMSA password automatically, and Windows-native Kerberos handles authentication. One managed identity can be shared across authorized application servers and administered with existing Active Directory tools.
gMSA suits Windows applications such as ASP.NET and ASP.NET Core apps, IIS application pools, Windows Services and background processes, and legacy .NET Framework or modern .NET applications across Windows Server farms.
Connect using Windows gMSA for password-less authentication:
using Alachisoft.NCache.Client;

var options = new CacheConnectionOptions();
options.Security = SecurityOptions.CreateWithGMSA();

ICache cache = CacheManager.GetCache("demoCache", options);
The application must run under an authorized gMSA identity.
Note: gMSA is supported for Cache Users (meaning NCache client applications). Node Admins authenticate with their Active Directory/LDAP user credentials.
Authentication in Azure, AWS & Google Cloud
NCache client applications on Windows Server VMs in Azure, AWS, and Google Cloud can authenticate through a managed Microsoft Active Directory service, self-managed domain controllers, or your existing on-premises Active Directory. Each managed service provides LDAP, Kerberos, and Windows domain capabilities, so your current Windows security model carries over to the cloud without a new NCache authentication model.
| Authentication Option | Azure | AWS | Google Cloud |
|---|---|---|---|
| Managed Microsoft AD | Entra Domain Services | AWS Managed Microsoft AD | Managed Microsoft AD |
| Self-Managed Active Directory | Azure VMs | EC2 | Compute Engine |
| On-Premises Active Directory | VPN / ExpressRoute | VPN / Direct Connect | Cloud VPN / Interconnect |
| LDAP Authentication | Supported | Supported | Supported |
| Kerberos / Windows gMSA | Available* | Available* | Available* |
| Windows Server VMs | Supported | Supported | Supported |
*Windows gMSA requires compatible domain services, domain configuration, and supported application/NCache integration. Validate specific managed-directory combinations before production deployment.
Role-Based Access Control (RBAC)
NCache separates administrative access from application cache access. NCache servers enforce permissions, so each authenticated identity can perform only the operations its access level allows.
- Node Admins: Create and configure cache clusters and server settings, add or remove authorized users and groups, and manage NCache through Management Center and PowerShell.
- Cache Users: Connect to authorized caches and add, update, retrieve, and remove data, but cannot administer servers or modify cluster configuration.
Permissions are assigned to Active Directory/LDAP users and groups at three boundaries: machine level (operating system administrators control local privileges), node level (who can manage NCache servers), and cache level (which applications and users can access each cache). This supports least privilege by keeping cache management separate from data access.
Add an Active Directory account as a Node Admin:
$nodeAdmin = Get-Credential

Add-NCacheUserOrGroup -Server 20.200.20.11 `
    -AccessLevel Admin `
    -NodeAdminCredentials $nodeAdmin `
    -UserOrGroupName david_watson `
    -UserOrGroupDN "CN=David Watson,OU=engineers,DC=example,DC=com" `
    -DomainController domain_controller
Grant that account Cache User access to a specific cache:
Add-NCacheUserOrGroup -Server 20.200.20.11 `
    -AccessLevel Cache `
    -CacheName defaultCache `
    -NodeAdminCredentials $nodeAdmin `
    -UserOrGroupName david_watson `
    -UserOrGroupDN "CN=David Watson,OU=engineers,DC=example,DC=com" `
    -DomainController domain_controller
These examples assume NCache security is enabled and the directory user exists. Replace the sample server, cache, account, distinguished name, and domain controller with your own values.
TLS / mTLS Secure Communication
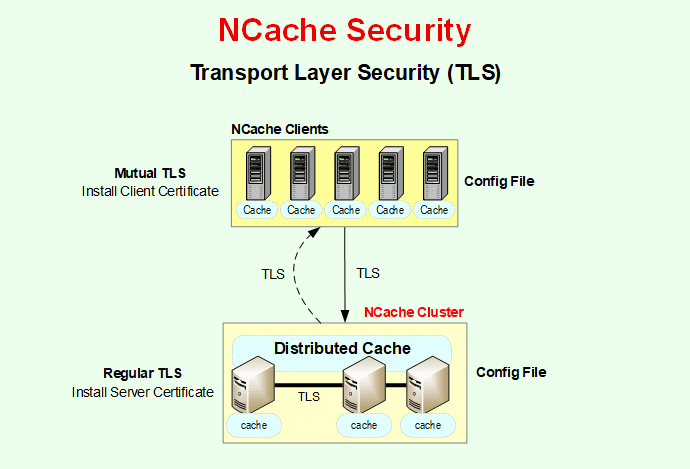
NCache encrypts network communication with TLS 1.2 and TLS 1.3 on Windows and Linux, protecting data in transit from interception. You can secure whichever paths your architecture requires: client-to-server, server-to-server within a cluster, Bridge traffic between geographically separated clusters, and supported management channels.
- Regular TLS: Encrypts traffic and lets clients verify the NCache server's certificate against a trusted Certificate Authority. Works with NCache-provided or enterprise-issued certificates.
- Mutual TLS (mTLS): Both endpoints present and validate trusted certificates, so clients without the required certificate cannot connect. mTLS complements LDAP authentication and NCache authorization; it does not replace application-level access controls.
Automatic TLS Certificate Management
NCache can generate, sign, and provision server certificates and renew them before they expire, with no manual replacement of certificate files. Each server keeps its own certificate and private key, and private keys never leave their machines. You can use certificates from your own Certificate Authority instead, and TLS/mTLS is configured the same way on Windows and Linux, which simplifies certificate management across many servers.
Data Encryption
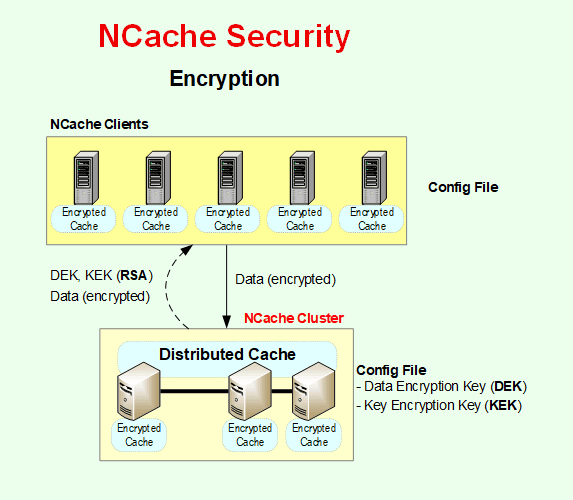
TLS protects data on the network; Data Encryption protects the cached data itself. When enabled, the NCache client SDK encrypts application data inside the client process before sending it to the cache servers, which keep it encrypted in memory and during replication. Authorized clients decrypt it transparently on retrieval, with no application coding involved. This protects confidential information even if cached data is accessed at the memory or storage level.
- Algorithms: AES-128, AES-192, and AES-256 (strong encryption for sensitive data); AES-FIPS for organizations with specific cryptographic requirements; 3DES for compatibility with legacy requirements.
- Key Management: A Data Encryption Key (DEK) encrypts cached data, a Key Encryption Key (KEK) protects the DEKs, and a Credentials Encryption Key (CEK) protects authentication credentials. RSA secures key and credential exchanges between NCache components. NCache manages the encryption process; administrators configure and protect the keys.
Secure NCache Management
Administrative access is authenticated and authorized separately from application cache access, so application users cannot perform management operations.
- NCache Management Center: Browser-based management with Active Directory/LDAP administrator authentication, node-level authorization, and HTTPS with TLS certificates (ASP.NET Core/Kestrel), on Windows and Linux.
- PowerShell: Local and remote administration with Active Directory/LDAP credentials, permissions enforced at NCache servers, and TLS-secured communication. Script cache and cluster security configuration and fit NCache into existing operational processes using familiar Windows tools.
Security for Linux, Docker & Kubernetes
TLS/mTLS and data encryption are available in all of these environments. Authentication and authorization depend on the deployment method.
- Linux: The full security model, without requiring Windows Server: Active Directory via LDAP, OpenLDAP and compatible directories, cloud-managed Microsoft AD, Node Admin and Cache User authorization at node and cache levels, TLS/mTLS, client-side encryption, and secure administrative access.
- Docker: TLS/mTLS with certificate-based endpoint authentication, client-side encryption, and LDAP authentication where supported and configured. Requires appropriate container networking, directory connectivity, and protection of configuration files, certificates, and keys.
- Kubernetes: Helm charts for on-premises Kubernetes, AKS, EKS, GKE, and OpenShift. TLS 1.2/1.3 and mTLS are configured through Helm, using Kubernetes Secrets for supported certificate configurations, alongside client-side encryption and Kubernetes networking and access controls on management and client endpoints.
Get Started
Whether you run legacy .NET Framework applications, modern .NET applications, or containerized workloads, NCache protects application access, network communication, and cached data using your existing Windows and Active Directory infrastructure, on-premises, in the cloud, or on Linux.
- Try NCache - Download and evaluate NCache.
- Configure Active Directory / LDAP Authentication - Secure administrator and application access.
- Configure Windows gMSA - Enable password-less Windows application authentication.
- Configure TLS / mTLS - Protect communication between NCache components.
- Configure Data Encryption - Encrypt sensitive cached data.
- Contact Us - Discuss enterprise security requirements.